Sustainability Frameworks, Standards and Regulations: The Buyer’s Guide to One Data Layer
Published
, 8 minute read
Share this article
Quick summary: Sustainability frameworks and standards explained learn how ESG, CSRD, OECD, and ISO frameworks work, why they matter, and how digital traceability enables compliance.
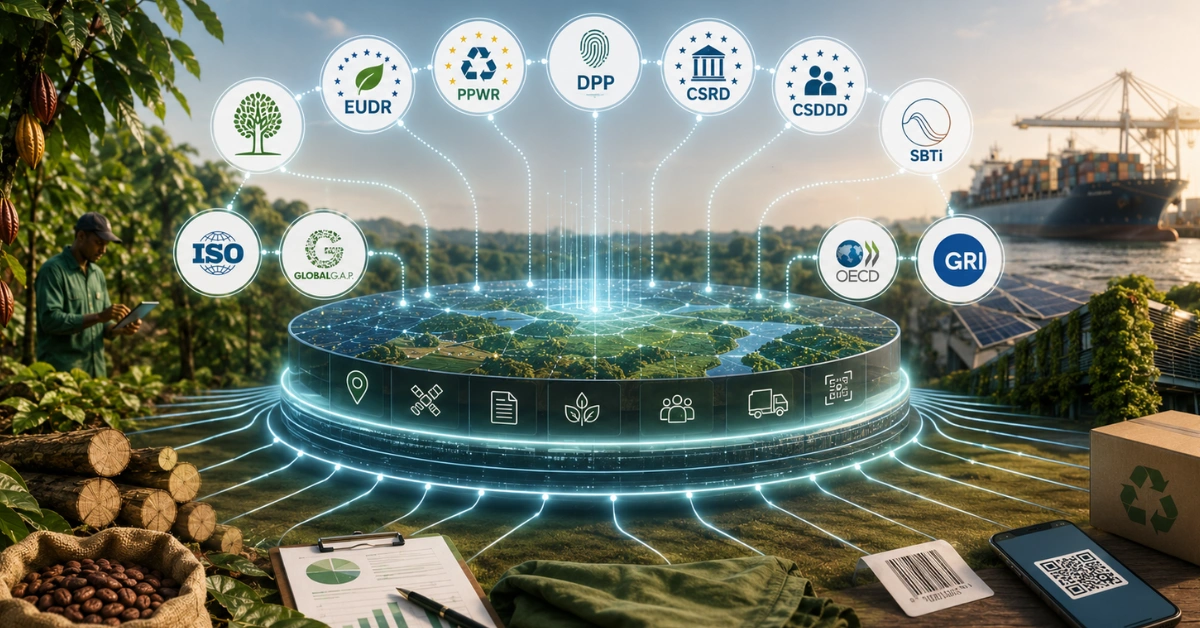
Sustainability frameworks, standards and regulations keep multiplying and every one of them seems to demand its own project, its own tool, and its own round of supplier emails. But here’s the executive insight most compliance conversations miss: they all ask for different reports, yet they nearly all depend on the same underlying data. The problem isn’t compliance. It’s that your data is scattered.
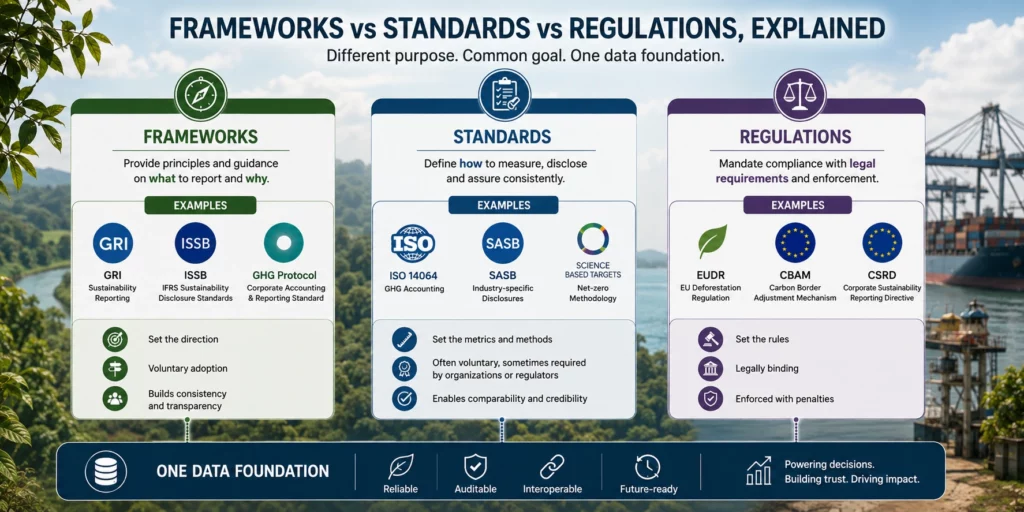
Frameworks (e.g. GRI, IFRS S1/S2, TNFD) define what to disclose. Standards (e.g. GHG Protocol, ISO 14064/14067, SBTi) define how to measure it. Regulations (e.g. EUDR, PPWR, ESPR/DPP, CBAM, CSRD, CSDDD) make specific disclosures legally mandatory with penalties. They differ in wording and reporting but they converge on the same foundational questions: where did this come from, who supplied it, how was it made, what’s its packaging, and what’s its carbon footprint? Answer those once, in one data layer, and you can feed all of them.
This guide is for the leader who owns that mess: the Chief Sustainability Officer, Head of Compliance, or supply-chain director tired of paying for EUDR software, PPWR software, carbon software, and a DPP tool that never talk to each other. We’ll show why sustainability frameworks, standards and regulations have become a data problem and how one data layer replaces the stack.
Key takeaways
Frameworks say what, standards say how, regulations make it mandatory — three layers, one vocabulary.
They ask different questions but need the same data: origin, supplier, process, packaging, emissions, chain of custody.
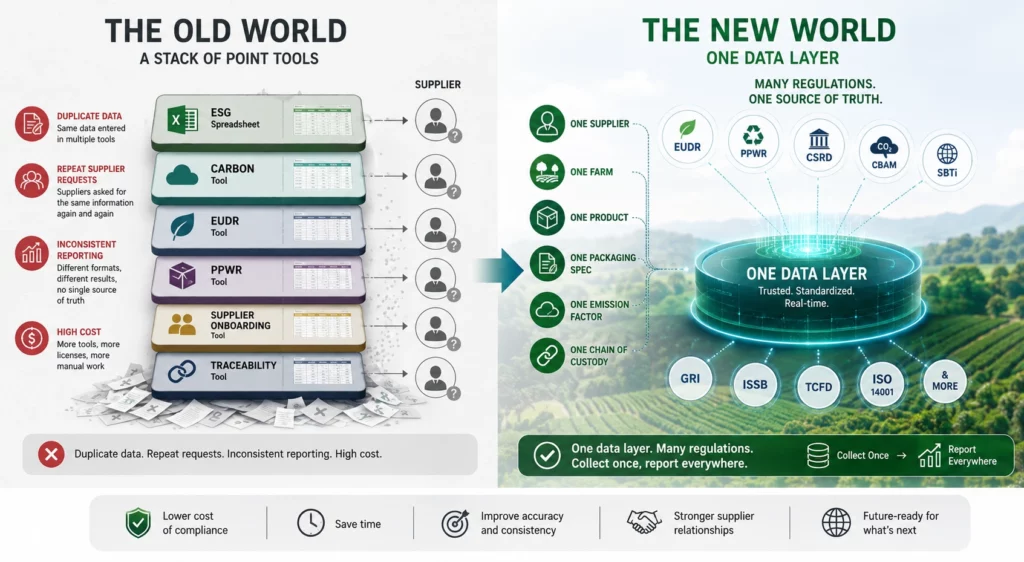
The old world is a stack of point tools — duplicate data, repeated supplier requests, inconsistent reporting, high cost.
The new world is one data layer, many regulations — collect once, report everywhere.
Buy a data foundation, not point solutions — it powers EUDR, PPWR, DPP, CBAM, CSRD, carbon and whatever comes next.
Simplify Regulatory Compliance with One Intelligent Platform
From EUDR and PPWR to Digital Product Passports and ESG reporting, TraceX helps businesses centralize compliance data, automate documentation, and build transparent, audit-ready supply chains all from a single platform.
Why Sustainability Has Become a Data Challenge, Not a Compliance Challenge
Most teams treat every new rule as a compliance challenge: read the regulation, hire the consultant, buy the tool. But if you line up today’s sustainability frameworks, standards and regulations side by side, the pattern is unmistakable they don’t actually disagree about the facts they need. They disagree about format, scope and deadline. The compliance text is different every time; the underlying data is the same every time.
That reframing matters because it changes what you should buy. If sustainability were a compliance challenge, the answer would be more compliance tools. Because it’s a data challenge, the answer is a data foundation that every regulation can draw from. Get the data layer right, and each new rule becomes a report you generate not a project you start from scratch.
Understanding the Sustainability Landscape: Frameworks vs Standards vs Regulations
The confusion starts because people lump three different things together. Separating sustainability frameworks, standards and regulations into their real roles is the fastest way to see the overlap:
Frameworks – they define what to disclose
Voluntary structures that shape what you report and how you tell the story. Examples: GRI, SASB, IFRS S1/S2 (ISSB), TCFD (now folded into ISSB), and TNFD for nature-related disclosure.
Standards – they define how to measure
The measurement rulebooks that make numbers comparable and defensible. Examples: the GHG Protocol, ISO 14064 and ISO 14067, SBTi, FSC and Rainforest Alliance. A standard tells you how to calculate a footprint or verify a claim.
Regulations – they make disclosure mandatory (with penalties)
Binding law. This is where EUDR comes in and it’s no longer optional. Examples: EUDR, PPWR, ESPR, Digital Product Passport (DPP), CBAM, CSRD and CSDDD. Miss these and you face fines, shipment delays, or lost EU market access.
Frameworks and standards ask you to report. Regulations make you prove. The moment a disclosure moves from framework to regulation, “we estimate” stops being acceptable. EUDR wants a geolocated plot; CBAM wants verified embedded emissions; DPP wants product-level data. That escalation from narrative to evidence is the whole reason a single, verifiable data layer beats a shelf of reporting tools.
Why Companies Struggle: Different Regulations, Same Questions
Put a compliance officer in a room with EUDR, PPWR, DPP, CBAM and CSRD and they’ll notice something uncomfortable: the regimes keep asking the same handful of questions in different clothing. Across the whole span of sustainability frameworks, standards and regulations, it comes down to six recurring questions:
Where did the product come from?
Who supplied it?
How was it manufactured?
What is the packaging?
What is the carbon footprint?
Which supplier provided the data and can you trust it?
Notice that not one of those is regulation-specific. They’re data questions. When teams answer them separately for each regime, they create the exact chaos the next section describes.
The Hidden Problem: Every Regulation Asks Differently, But Needs the Same Data
Here is the old world most sustainability teams still live in and the new world the smart ones are moving to:
The reason the new world works is that a small set of foundational data objects is reused across almost every regime. Map them once and the overlap becomes obvious:
Foundational data object
EUDR
PPWR
DPP / ESPR
CBAM
CSRD / ESG
Carbon
Supplier Master
✓
✓
✓
✓
✓
Product Master
✓
✓
✓
✓
Packaging Data
✓
✓
✓
Farm / Origin Data
✓
✓
✓
✓
Chain of Custody
✓
✓
✓
✓
Emission Factors
✓
✓
✓
✓
You don’t have six compliance problems. You have one data model, queried six ways. Every column in that matrix is a report. Every row is a piece of data you already collect or should. Companies that buy a tool per column end up storing the same supplier six times and emailing that supplier six times. Companies that build the rows once answer every column from a single source of truth.
One Data Layer: A Sustainability Intelligence Layer, Not Point Software
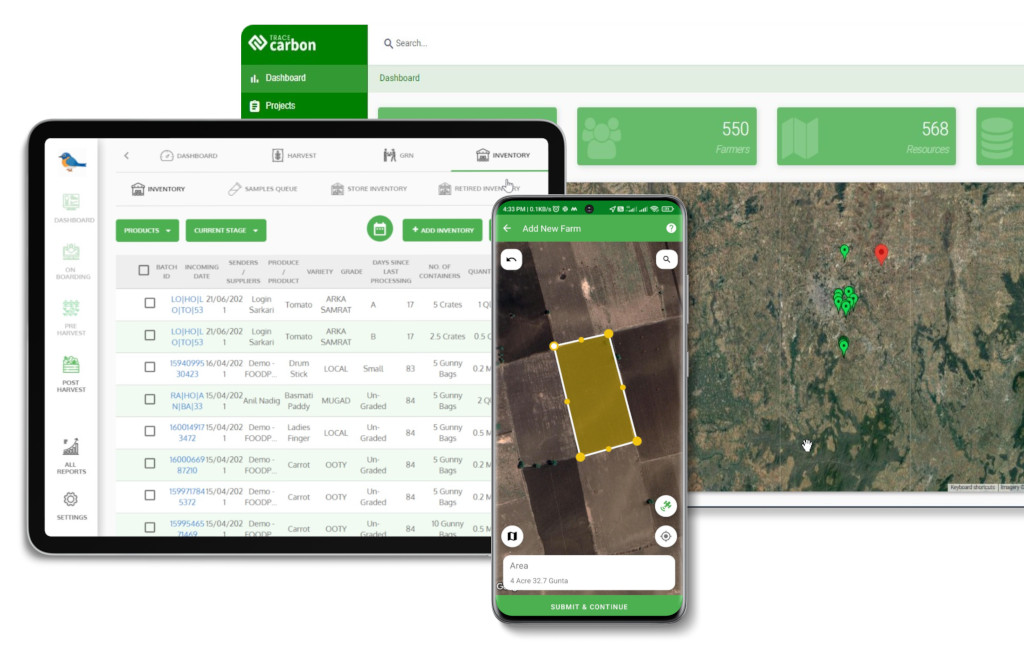
This is where the buying decision inverts. Instead of shopping for EUDR software, then PPWR software, then carbon software, then a DPP tool each with its own supplier onboarding and its own data silo you buy the layer underneath all of them. Against the full sweep of sustainability frameworks, standards and regulations, TraceX positions as a Sustainability Intelligence Layer: one place where supplier, farm, product, packaging, emission and custody data live, connect, and feed every report.
Feature → Benefit, mapped to the pain
Single supplier & farm onboarding — collect data once; stop emailing the same supplier for every regulation.
Unified product, packaging & emissions records — one product master that PPWR, DPP, CBAM and ESG all draw from
Chain of custody with geolocation — the EUDR/DPP backbone, reused for ESG and carbon claims.
Many report views from one dataset — generate EUDR DDS, PPWR, DPP, CBAM and CSRD outputs without re-collecting data.
Immutable, audit-ready evidence — blockchain-backed records that stand up to third-party assurance and future regulations.
What if EUDR, PPWR, DPP, CBAM and CSRD all ran off the same supplier, product and origin data collected once? Book a demo and we’ll map your sustainability frameworks, standards and regulations onto one data layer.
Point Solutions vs One Data Layer: A Buyer’s Comparison
Consideration
Stack of point tools
One data layer
Supplier onboarding
Repeated per tool
Once, reused everywhere
Data storage
Duplicated & inconsistent
Single source of truth
New regulation
Buy another tool
Add a report view
Reporting consistency
Conflicting numbers
One dataset, aligned outputs
Audit & assurance
Scattered evidence
Immutable, audit-ready
Total cost of ownership
Rises with each regime
Amortised across all regimes
Future-proofing
Reactive, per-rule
Ready for the next regulation
Sustainability Data Layer: A Buyer’s Evaluation Checklist
Before you sign, pressure-test any “intelligence layer” vendor against these:
Does it store supplier, product, packaging, farm, custody and emissions data in one model?
Does it onboard a supplier once and reuse that record across regulations?
Can it generate EUDR, PPWR, DPP, CBAM and CSRD outputs from the same dataset?
Does it capture geolocation and chain of custody to evidence standard?
Are records immutable and audit-ready for third-party assurance?
Does it integrate with existing ERP/systems instead of adding a silo?
Can it absorb the next regulation without a new tool purchase?
Frequently Asked Questions (FAQ’s)
What’s the difference between sustainability frameworks, standards and regulations?
Frameworks define what to disclose (GRI, ISSB, TNFD); standards define how to measure it (GHG Protocol, ISO 14064/14067, SBTi); regulations make specific disclosures legally mandatory with penalties (EUDR, PPWR, ESPR/DPP, CBAM, CSRD, CSDDD).
Why is sustainability a data challenge, not a compliance challenge?
Because the regimes differ in format and deadline but converge on the same underlying data origin, supplier, process, packaging, emissions, chain of custody. Fix the data once and compliance becomes a reporting task.
What is a sustainability data layer?
A single, verifiable store of foundational data objects supplier, product, packaging, farm, custody, emissions that every framework, standard and regulation can draw from, so you collect once and report everywhere.
Which regulations can one data layer support?
The same foundation supports EUDR, PPWR, ESPR/DPP, CBAM, CSRD and CSDDD, plus voluntary carbon and ESG reporting and is positioned to absorb future regulations without new tools.
Isn’t buying point tools per regulation faster to start?
It feels faster for the first regulation and gets slower for every one after duplicate data, repeated supplier requests, and conflicting numbers. A data layer costs a little more up front and far less across the full regulatory wave.
Start using TraceX
Transparency, Trust, & Success for your Climate Journey.
We use cookies on our website to give you the most relevant experience by remembering your preferences and repeat visits. By clicking “Accept All”, you consent to the use of ALL the cookies. However, you may visit "Cookie Settings" to provide a controlled consent.
This website uses cookies to improve your experience while you navigate through the website. Out of these, the cookies that are categorized as necessary are stored on your browser as they are essential for the working of basic functionalities of the website. We also use third-party cookies that help us analyze and understand how you use this website. These cookies will be stored in your browser only with your consent. You also have the option to opt-out of these cookies. But opting out of some of these cookies may affect your browsing experience.
Necessary cookies are absolutely essential for the website to function properly. These cookies ensure basic functionalities and security features of the website, anonymously.
Cookie
Duration
Description
cookielawinfo-checkbox-analytics
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Analytics".
cookielawinfo-checkbox-functional
11 months
The cookie is set by GDPR cookie consent to record the user consent for the cookies in the category "Functional".
cookielawinfo-checkbox-necessary
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookies is used to store the user consent for the cookies in the category "Necessary".
cookielawinfo-checkbox-others
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Other.
cookielawinfo-checkbox-performance
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Performance".
viewed_cookie_policy
11 months
The cookie is set by the GDPR Cookie Consent plugin and is used to store whether or not user has consented to the use of cookies. It does not store any personal data.
Functional cookies help to perform certain functionalities like sharing the content of the website on social media platforms, collect feedbacks, and other third-party features.
Performance cookies are used to understand and analyze the key performance indexes of the website which helps in delivering a better user experience for the visitors.
Analytical cookies are used to understand how visitors interact with the website. These cookies help provide information on metrics the number of visitors, bounce rate, traffic source, etc.
Advertisement cookies are used to provide visitors with relevant ads and marketing campaigns. These cookies track visitors across websites and collect information to provide customized ads.
Download the 2026 Traceability Scorecard and Benchmark Your Supply Chain Across 10 Critical Capabilities.
Download our eBook
Don’t Wait for an Audit to Find Your EUDR Gaps
The 2026 Simplification Package changes how HS codes, DDS pass-through and geolocation rules apply to you. Get the free guide and 20-point readiness checklist before enforcement catches you unprepared.