Supply Chain Due Diligence: How to Build an Audit-Ready Program for EUDR, CSDDD and Beyond
Published
, 7 minute read
Share this article
Quick summary: Supply chain due diligence made audit-ready: see what EUDR, CSDDD and the Forced Labour Regulation require, the 6-step process, and how software closes gaps.
Supply chain due diligence is the ongoing process of identifying, preventing and documenting human rights, environmental and legality risks across every tier of your suppliers. EUDR, CSDDD, the EU Forced Labour Regulation and national laws such as Germany’s LkSG now require companies to prove that process with records, not policies.
Key Takeaways
Due diligence is continuous: map, assess, mitigate, monitor and document, then repeat.
EUDR applies from 30 December 2026 for large and medium operators; CSDDD applies from 26 July 2029 to companies with more than 5,000 employees and over EUR 1.5 billion turnover.
Suppliers of in-scope companies will face questionnaires and evidence requests well before those dates.
Certifications support risk mitigation but do not replace supplier-level and plot-level evidence.
A due diligence platform replaces spreadsheet chasing with risk scoring and audit-ready records
Supply chain due diligence used to mean a supplier code of conduct and an annual audit sample. Regulators now expect a documented, risk-based process that reaches past Tier 1 suppliers and produces evidence on request.
Identify supplier risks, improve supply-chain transparency, and build more responsible sourcing practices with TraceX.
Connect with our experts to explore how digital traceability and sustainability solutions can support your supplier due diligence processes.
Supply Chain Due Diligence Explained: What It Is and What It Covers
Supply chain due diligence is a structured, repeatable process for finding and addressing risks linked to your suppliers, from deforestation and illegal harvesting to forced labour and unsafe working conditions.
Most laws build on the OECD Due Diligence Guidance for Responsible Business Conduct, so supply chain due diligence follows the same logic in every regime. Companies are expected to:
Embed responsible sourcing into policies and supplier contracts
Identify and assess actual and potential adverse impacts
Prevent, mitigate or stop those impacts
Track whether the measures work
Communicate what was done and provide for remediation
Supply Chain Due Diligence Laws: What Applies and When
Several regimes now overlap, each with its own scope and evidence standard.
The practical effect is that one supply chain due diligence program has to satisfy several authorities at once.
Regulation
Applies from
What it expects
EUDR, Reg. (EU) 2023/1115 as amended by 2025/2650
30 Dec 2026 (large/medium); 30 Jun 2027 (micro/small)
Plot geolocation, deforestation-free and legality evidence, risk assessment, due diligence statement
CSDDD, Directive (EU) 2024/1760 as amended by 2026/470
26 Jul 2029 (transposition by 26 Jul 2028)
Risk-based human rights and environmental due diligence for EU firms over 5,000 staff and EUR 1.5bn turnover
Forced Labour Regulation (EU) 2024/3015
14 Dec 2027
Market ban on forced-labour products; traceability helps defend products in investigations
EU Battery Regulation (EU) 2023/1542
Due diligence 18 Aug 2027
Raw material due diligence for cobalt, lithium, nickel and natural graphite
Germany LkSG
In force since 2023
Risk analysis, prevention and documentation; BAFA reporting being abolished
US UFLPA
In force since June 2022
Presumption that goods linked to Xinjiang involve forced labour unless rebutted
Even if your company sits below the CSDDD thresholds, your largest customers do not. Expect their supply chain due diligence requests to reach you first.
EUDR and the Corporate Sustainability Due Diligence Directive (CSDDD) address different aspects of responsible business conduct, from deforestation-free sourcing to identifying and addressing human rights and environmental impacts across value chains. Discover their key differences, overlapping requirements, and how businesses can strengthen compliance processes through better supply-chain visibility, risk assessment, and traceability.
Supply Chain Due Diligence Process: Six Steps That Hold Up in an Audit
An audit-ready process moves from mapping to evidence in six repeatable steps.
Map suppliers across tiers: link each supplier to sites, materials and product flows, not just contracts.
Collect origin and legality evidence: geolocation, land-use records, permits and certificates tied to specific lots.
Score risk: combine country, commodity and supplier factors, including satellite deforestation checks where relevant.
Mitigate: request more data, run audits, train suppliers or suspend sourcing from high-risk plots.
Monitor continuously: set alerts for expired documents, new risk signals and changes in supplier status.
Document and report: keep a retrievable record of every decision and file statements such as the EUDR DDS.
A global tire manufacturer applied this model to natural rubber, combining remote-sensing risk assessment, geolocation traceability and integration with the EU Information System to support supply chain due diligence for EUDR.
EUDR due diligence requires businesses to collect accurate supply-chain information, verify geolocation data, assess deforestation and legality risks, and take appropriate mitigation measures. Discover the key steps, documentation requirements, and digital solutions that can help your business strengthen EUDR readiness and improve supply-chain transparency.
Supply Chain Due Diligence Mistakes That Fail Audits
Most supply chain due diligence failures trace back to five avoidable habits.
Relying on certificates alone: FSC, Fairtrade or RSPO support mitigation but do not replace plot-level geolocation or an EUDR due diligence statement
Stopping at Tier 1: the highest risks usually sit with traders, collectors and smallholders upstream
Running on spreadsheets and email: versions multiply, deadlines slip and evidence cannot be retrieved quickly
Missing documents: land-use records, permits and risk reports absent when an authority asks
Reacting only when asked: rushed file assembly after a request, instead of continuous monitoring
Each gap turns an authority request or customer audit into days of manual work, and under EUDR can mean a blocked shipment and penalties.
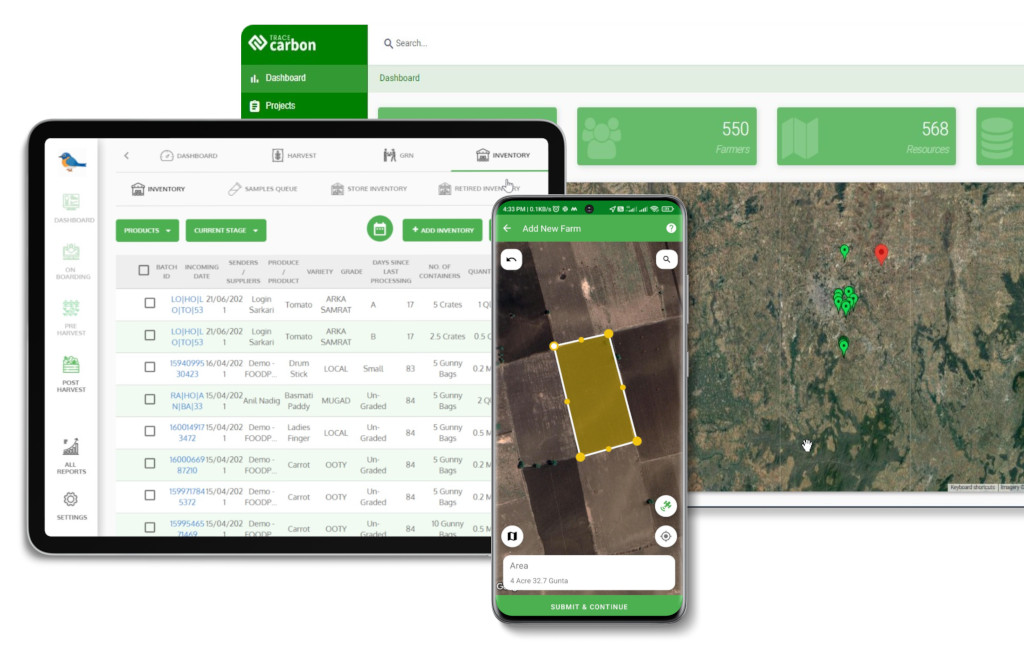
Due diligence works when it runs inside daily sourcing, not as a year-end exercise. When supplier onboarding, field data, risk scoring and documentation live in one system, the answer to any regulator or customer request already exists. The TraceX platform is built on that principle, and TraceX EUDR Solutions applies it to EUDR due diligence statements,
See supply chain due diligence automated end to end.
Supply Chain Due Diligence Software vs Manual Processes
Manual processes can record due diligence; they struggle to prove it at scale.
Capability
Manual (spreadsheets, email)
TraceX platform
Multi-tier supplier mapping
Tier 1 only, static lists
Suppliers linked to sites, plots and lots
Risk assessment
Annual questionnaire review
Automated scoring with satellite and country risk data
Evidence collection
Chasing files by email
Supplier and field app capture with validation
Monitoring
Periodic audits
Alerts for expired documents and new risk signals
Reporting
Days of manual assembly
Audit-ready reports and EUDR DDS workflows
Moving supply chain due diligence onto a platform shortens response times, reduces audit preparation and gives procurement teams a defensible basis for sourcing decisions
Supply Chain Due Diligence Software: Buyer Evaluation Checklist
Evaluate vendors on the evidence they produce, not the dashboards they show.
Does it map suppliers beyond Tier 1, down to plots or sites?
Can it validate EUDR geolocation (GeoJSON) and run deforestation checks?
Does risk scoring combine country, commodity and supplier factors?
Can smallholders and small suppliers submit data offline via mobile?
Does it track mitigation actions and document expiry automatically?
Can it cover EUDR, CSDDD and forced labour requirements in one data model?
Does it integrate with your ERP and the EU Information System?
A platform that meets all seven gives you supply chain due diligence you can defend in front of any authority.
Frequently Asked Questions
What is supply chain due diligence?
Supply chain due diligence is the ongoing process of identifying, preventing and documenting human rights, environmental and legality risks linked to your suppliers.
Which laws require supply chain due diligence?
Key regimes include EUDR, CSDDD, the EU Forced Labour Regulation, the EU Battery Regulation, Germany’s LkSG and the US UFLPA.
When does CSDDD apply?
After Omnibus I, CSDDD applies from 26 July 2029 to EU companies with more than 5,000 employees and over EUR 1.5 billion turnover, and non-EU firms with over EUR 1.5 billion EU turnover.
Does CSDDD affect suppliers outside its scope?
Indirectly, yes. In-scope customers will request data and commitments from business partners, although Omnibus I limits how much they can ask of smaller companies.
Are certifications enough for EUDR due diligence?
No. Certifications support risk mitigation, but EUDR still requires plot geolocation, legality evidence and a due diligence statement for each placement.
How often should supply chain due diligence be updated?
Continuously. Risk data, documents and supplier status change, so monitoring should run year-round with formal reviews at least annually or when risks change.
What should supply chain due diligence software include?
We use cookies on our website to give you the most relevant experience by remembering your preferences and repeat visits. By clicking “Accept All”, you consent to the use of ALL the cookies. However, you may visit "Cookie Settings" to provide a controlled consent.
This website uses cookies to improve your experience while you navigate through the website. Out of these, the cookies that are categorized as necessary are stored on your browser as they are essential for the working of basic functionalities of the website. We also use third-party cookies that help us analyze and understand how you use this website. These cookies will be stored in your browser only with your consent. You also have the option to opt-out of these cookies. But opting out of some of these cookies may affect your browsing experience.
Necessary cookies are absolutely essential for the website to function properly. These cookies ensure basic functionalities and security features of the website, anonymously.
Cookie
Duration
Description
cookielawinfo-checkbox-analytics
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Analytics".
cookielawinfo-checkbox-functional
11 months
The cookie is set by GDPR cookie consent to record the user consent for the cookies in the category "Functional".
cookielawinfo-checkbox-necessary
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookies is used to store the user consent for the cookies in the category "Necessary".
cookielawinfo-checkbox-others
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Other.
cookielawinfo-checkbox-performance
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Performance".
viewed_cookie_policy
11 months
The cookie is set by the GDPR Cookie Consent plugin and is used to store whether or not user has consented to the use of cookies. It does not store any personal data.
Functional cookies help to perform certain functionalities like sharing the content of the website on social media platforms, collect feedbacks, and other third-party features.
Performance cookies are used to understand and analyze the key performance indexes of the website which helps in delivering a better user experience for the visitors.
Analytical cookies are used to understand how visitors interact with the website. These cookies help provide information on metrics the number of visitors, bounce rate, traffic source, etc.
Advertisement cookies are used to provide visitors with relevant ads and marketing campaigns. These cookies track visitors across websites and collect information to provide customized ads.
Download the 2026 Traceability Scorecard and Benchmark Your Supply Chain Across 10 Critical Capabilities.
Download our eBook
Don’t Wait for an Audit to Find Your EUDR Gaps
The 2026 Simplification Package changes how HS codes, DDS pass-through and geolocation rules apply to you. Get the free guide and 20-point readiness checklist before enforcement catches you unprepared.