Supply Chain Compliance: Collect Supplier Evidence Once, Prove It Everywhere
Published
, 8 minute read
Share this article
Quick summary: Supply chain compliance for EUDR, PPWR, CSRD and battery rules: collect supplier evidence once and reuse it for every audit. Get the 2026 buyer checklist.
Supply chain compliance is the ability to prove, with verifiable records, that every supplier, material and product in your network meets the legal requirements of the markets you sell into. In the EU, that now means answering the same four questions (who supplied it, what it is, where it came from and when it moved) for EUDR, PPWR, the Battery Regulation, ESPR and CSRD. Companies that build one shared evidence layer spend far less effort per audit than companies running a separate spreadsheet for each rule.
KEY TAKEAWAYS
PPWR has applied since 12 August 2026, EUDR applies from 30 December 2026 for large and medium operators, and the battery passport becomes mandatory on 18 February 2027.
Every one of these rules asks for the same core facts: supplier identity, material, origin and chain of custody.
Omnibus I narrowed CSRD to companies above 1,000 employees and €450 million turnover and limited what they can demand from smaller suppliers.
Tier-1 declarations are no longer evidence. EUDR needs plot geolocation; batteries need upstream due diligence.
Supply chain compliance software pays for itself when one supplier record serves several regulations.
Move beyond spreadsheets and fragmented processes with TraceX’s regulatory compliance solutions.
From traceability, supplier data, geolocation, risk assessment, evidence management, and compliance reporting.
Supply Chain Compliance Deadlines: Why 2026 Is the Crunch Year
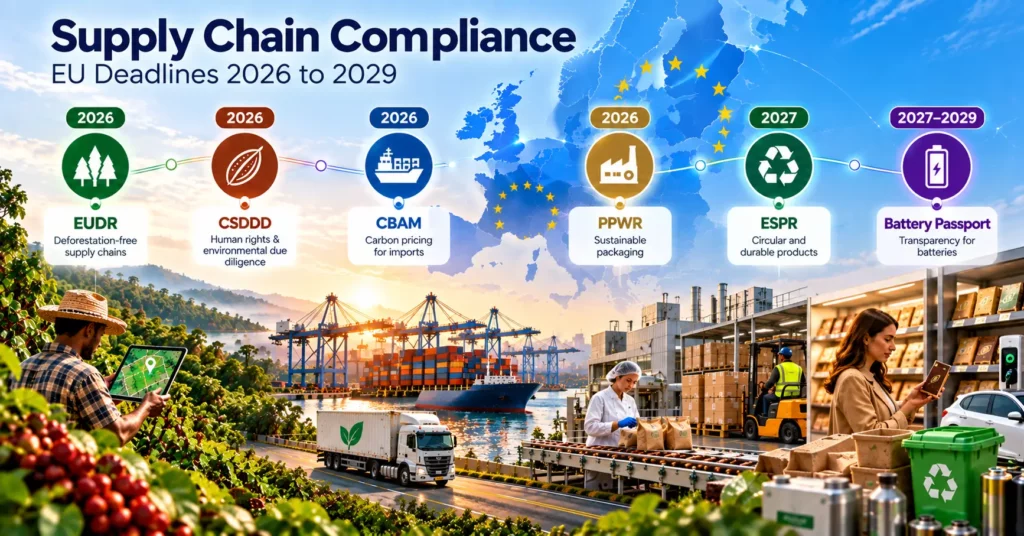
Six EU regimes now overlap, so compliance can no longer run as separate projects.
Which regulations apply, and when
What each one asks you to prove
Supply chain compliance used to mean passing an annual supplier audit. That model broke once EU rules began asking for shipment-level and product-level evidence. PPWR moved into general application on 12 August 2026. EUDR follows on 30 December 2026 for large and medium operators and traders. The battery passport arrives on 18 February 2027.
Regulation
What you must prove
Key date
EUDR (Reg. (EU) 2023/1115, amended by 2025/2650)
Deforestation-free origin after 31 December 2020, plot geolocation, legality of production
30 Dec 2026 (large/medium); 30 Jun 2027 (micro/small); 30 Dec 2027 for products newly added to Annex I
PPWR (Reg. (EU) 2025/40)
Packaging conformity, technical documentation, EU Declaration of Conformity
12 Aug 2026 (general application)
Battery Regulation (Reg. (EU) 2023/1542)
Battery passport data; raw material due diligence
18 Feb 2027 (passport); 18 Aug 2027 (due diligence)
ESPR (Reg. (EU) 2024/1781)
Digital Product Passport data for each regulated product group
Set product group by product group through delegated acts
CSRD (as amended by Directive (EU) 2026/470)
Value chain sustainability disclosures
Companies above 1,000 employees and €450m turnover
CSDDD (Directive (EU) 2024/1760, as amended)
Risk-based human rights and environmental due diligence
26 Jul 2029
Supply Chain Compliance Gaps: Where Most Programmes Break
Three failure points show up in almost every audit, and none of them is a shortage of data.
Supplier records that do not connect
Visibility that stops at Tier 1
A separate project for every regulation
Compliance Data Scattered Across Systems
Supplier facts live in email threads, ERP tables, certificate PDFs and spreadsheets, with no shared identifier linking them. When a competent authority asks which plots fed a specific shipment, teams rebuild the answer by hand.
Compliance Visibility That Stops at Tier 1
Most companies know their direct suppliers and little beyond them. EUDR needs the plot of land. The Battery Regulation expects due diligence on upstream raw materials. A Tier-1 letter stating that all inputs comply is a claim, not evidence.
Compliance Run as One Project per Regulation
The costliest supply chain compliance gap is organisational. When the EUDR team, the packaging team and the ESG team each send suppliers their own questionnaire, suppliers answer the same questions three times, often inconsistently. Auditors then see three versions of the truth.
The biggest risk in supply chain compliance is rarely missing data. It is conflicting data that nobody reconciled before the audit.
Supply Chain Compliance Built on Event-Based Traceability
A shared data model captures each supplier fact once and reuses it wherever a regulation asks for it.
How event records form a chain of custody
Why standard identifiers matter
How one record feeds many outputs
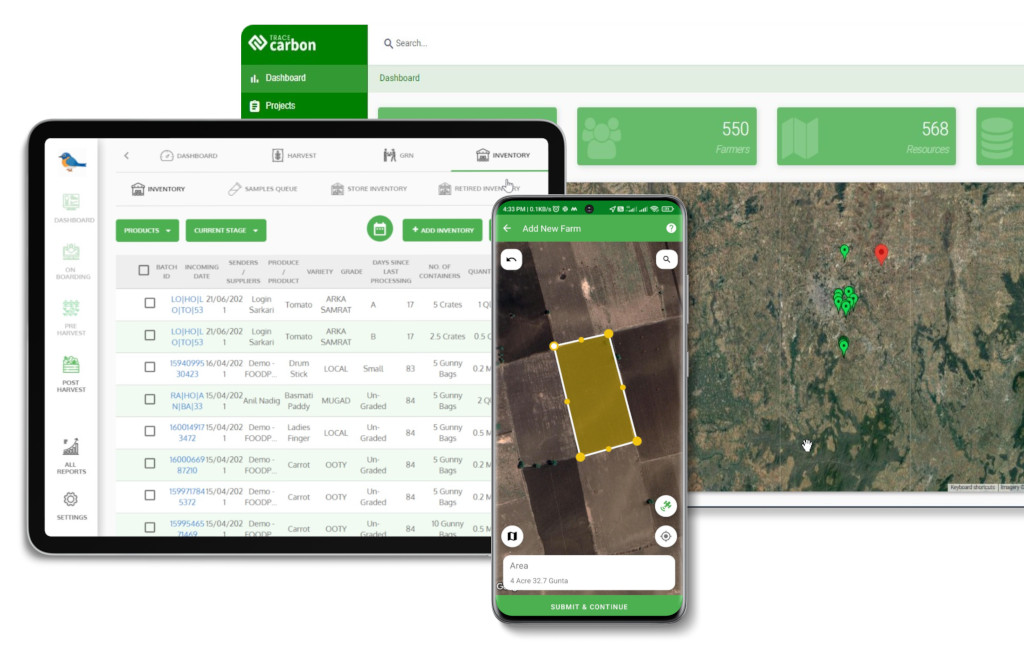
Event-based traceability records every meaningful change in a product’s life as a data event: what (the batch or unit), where (the farm polygon, factory or warehouse), when (a timestamp) and who (a verified supplier identity). Linked in sequence, these events form the chain of custody.
GS1 identifiers give each entity one persistent reference: GLNs for suppliers and sites, GTINs for products and SSCCs for logistics units. A harvest event in Côte d’Ivoire and a receiving event in Rotterdam then point at the same batch. Our guide to GS1 standards for traceability explains the setup.
Traceability Records That Serve Several Regulations
The same plot polygon supports the due diligence statement that the EU operator files under EUDR. The same material declaration feeds a PPWR technical file. The same smelter record supports battery due diligence. Note that the EU DPP registry stores only identifiers; the full product data stays in the passport system.
Traceability Checks That Run Continuously
Validation rules at the point of supplier entry catch a missing geolocation or an expired certificate before goods ship, not after an authority asks. That is the practical meaning of continuous supply chain compliance.
Stop buying compliance one regulation at a time. Every new EU rule tempts teams to add another point tool, and we think that is the most expensive route to supply chain compliance. Build one supplier evidence layer, then treat each regulation as an output of it.
Omnibus I makes this more urgent. Large reporting companies can no longer push smaller suppliers for data beyond voluntary standards, so each answer you do get has to serve every obligation it can.
Supply Chain Compliance Software vs Manual Tracking
Spreadsheets hold up for one regulation and one tier; they fail once either number grows.
Capability
Spreadsheets and email
TraceX platform
Supplier onboarding
A new questionnaire per regulation, re-sent each year
One digital supplier profile reused across regulations
Upstream visibility
Tier-1 declarations only
Multi-tier mapping down to plot, site or smelter
Geolocation evidence
Coordinates pasted into cells, rarely validated
Polygon capture with format and overlap checks
Chain of custody
Reconstructed after the fact
Recorded as batch events at each handover
Audit response
Days of searching through files
Filtered export by shipment, batch or product
Regulatory change
Manual rework after every amendment
Rules updated centrally
The tipping point for supply chain compliance software usually arrives with the second regulation. Once suppliers are answering overlapping questions for two teams, a shared platform costs less than the rework it replaces. For EUDR due diligence statement workflows specifically, TraceX EUDR Solutions prepares the data the EU operator needs to file.
See how one supplier record maps to EUDR, PPWR and battery passport outputs.
Supply chain compliance means proving, with verifiable records, that your suppliers, materials and products meet the rules of the markets you sell into. In the EU, that now means shipment-level evidence, not annual declarations.
Which EU regulations affect supply chain compliance in 2026 and 2027?
PPWR (since 12 August 2026), EUDR (30 December 2026 for large and medium operators), the battery passport (18 February 2027), ESPR product passports, CSRD for the largest companies and CSDDD from 26 July 2029.
Does CSRD still apply to my company after Omnibus I?
Directive (EU) 2026/470 limits CSRD reporting to companies with more than 1,000 employees and over €450 million in net turnover. Smaller suppliers can still receive customer data requests, capped at voluntary standards.
Are RSPO or FSC certifications enough for EUDR?
No. Certifications support risk assessment and mitigation, but they do not replace the plot geolocation, due diligence statement and product-level evidence that EUDR requires.
Who files the EUDR due diligence statement?
The EU operator placing the product on the market files the statement. Exporters and upstream suppliers provide the geolocation and origin data that the statement relies on.
How far upstream does supply chain visibility need to go?
As far as the regulation requires: the plot of land for EUDR, raw material sourcing for batteries. Start with high-risk commodities and regions, then expand tier by tier.
What should we prioritise first?
Start with the nearest, highest-exposure deadline, map those suppliers to origin, and structure the data so the next regulation can reuse it.
Start using TraceX
Transparency, Trust, & Success for your Climate Journey.
We use cookies on our website to give you the most relevant experience by remembering your preferences and repeat visits. By clicking “Accept All”, you consent to the use of ALL the cookies. However, you may visit "Cookie Settings" to provide a controlled consent.
This website uses cookies to improve your experience while you navigate through the website. Out of these, the cookies that are categorized as necessary are stored on your browser as they are essential for the working of basic functionalities of the website. We also use third-party cookies that help us analyze and understand how you use this website. These cookies will be stored in your browser only with your consent. You also have the option to opt-out of these cookies. But opting out of some of these cookies may affect your browsing experience.
Necessary cookies are absolutely essential for the website to function properly. These cookies ensure basic functionalities and security features of the website, anonymously.
Cookie
Duration
Description
cookielawinfo-checkbox-analytics
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Analytics".
cookielawinfo-checkbox-functional
11 months
The cookie is set by GDPR cookie consent to record the user consent for the cookies in the category "Functional".
cookielawinfo-checkbox-necessary
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookies is used to store the user consent for the cookies in the category "Necessary".
cookielawinfo-checkbox-others
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Other.
cookielawinfo-checkbox-performance
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Performance".
viewed_cookie_policy
11 months
The cookie is set by the GDPR Cookie Consent plugin and is used to store whether or not user has consented to the use of cookies. It does not store any personal data.
Functional cookies help to perform certain functionalities like sharing the content of the website on social media platforms, collect feedbacks, and other third-party features.
Performance cookies are used to understand and analyze the key performance indexes of the website which helps in delivering a better user experience for the visitors.
Analytical cookies are used to understand how visitors interact with the website. These cookies help provide information on metrics the number of visitors, bounce rate, traffic source, etc.
Advertisement cookies are used to provide visitors with relevant ads and marketing campaigns. These cookies track visitors across websites and collect information to provide customized ads.
Download the 2026 Traceability Scorecard and Benchmark Your Supply Chain Across 10 Critical Capabilities.
Download our eBook
Don’t Wait for an Audit to Find Your EUDR Gaps
The 2026 Simplification Package changes how HS codes, DDS pass-through and geolocation rules apply to you. Get the free guide and 20-point readiness checklist before enforcement catches you unprepared.