Battery DPP Architecture: How the Data Model Actually Works
Published
, 9 minute read
Share this article
Quick summary: Battery DPP architecture explained: the four layers, GS1 and EPCIS standards, and the unique identifier that makes a 2027-ready battery passport work.
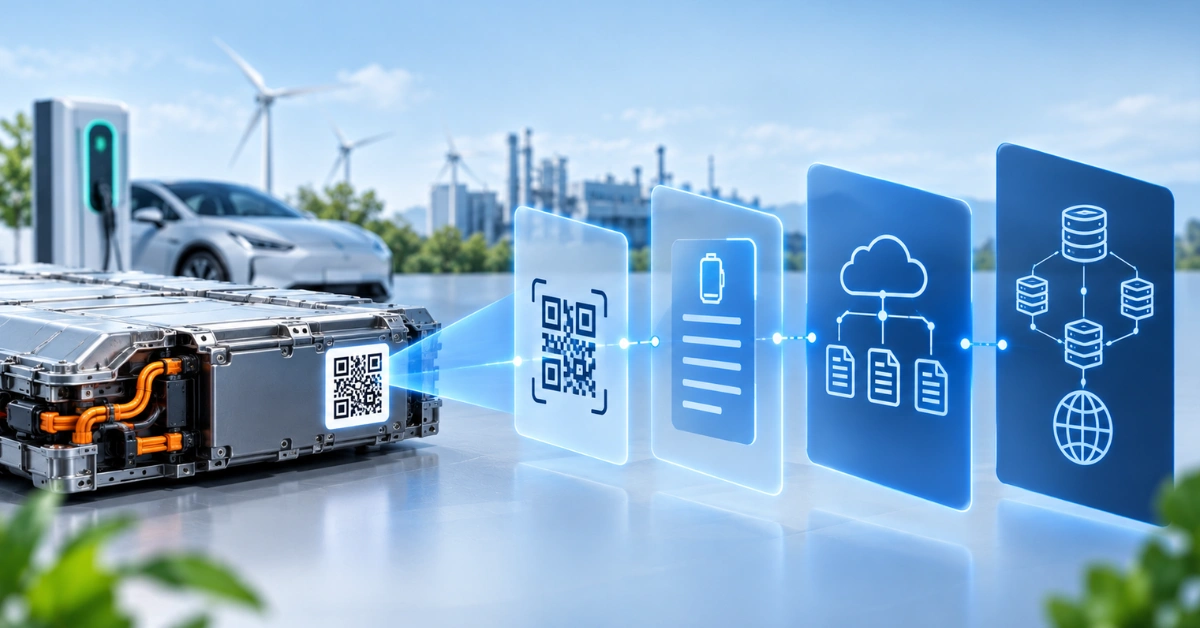
Battery DPP architecture is the layered technical structure that connects a physical battery to its regulated lifecycle data. It has four working parts: a data carrier (the QR code) on the battery, a persistent unique identifier that never changes, a decentralized data layer where economic operators hold the actual passport data, and a thin EU registry that stores identifiers so authorities can locate each passport. Under Article 77 of Regulation (EU) 2023/1542, this structure becomes mandatory on 18 February 2027 for EV, light-means-of-transport, and industrial batteries above 2 kWh.
KEY TAKEAWAYS
Decentralized by design. No single EU database holds passport data. Economic operators keep it and expose it through the identifier, which removes a single point of failure and protects commercially sensitive information.
The identifier is the root node. A persistent unique identifier ties the data carrier, the registry entry, and every data record together, and it does not change across the battery’s life.
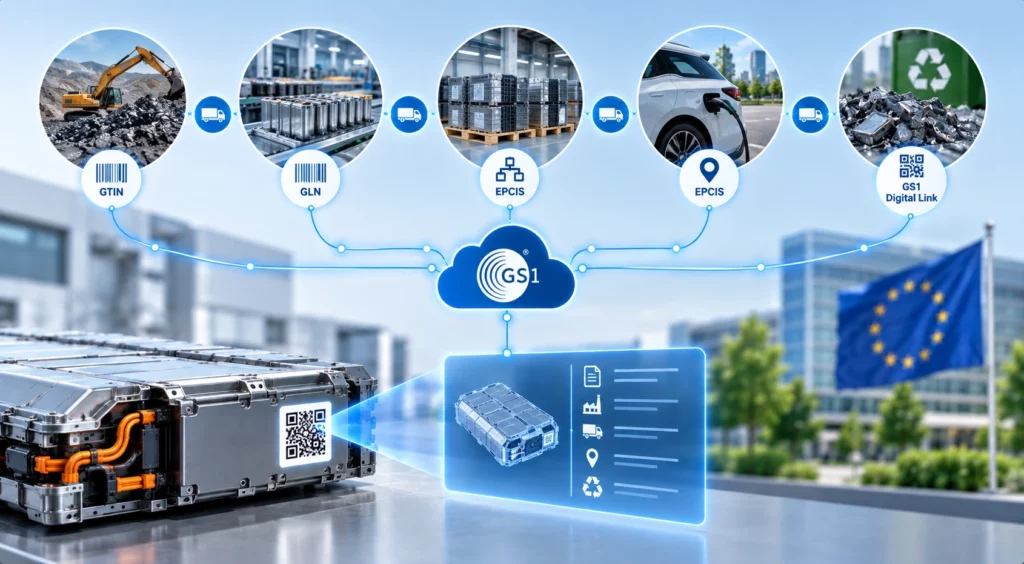
GS1 standards do the heavy lifting. GTIN identifies the battery, GLN identifies sites, EPCIS records lifecycle events, and GS1 Digital Link resolves the identifier to data.
The registry stores identifiers, not compliance proof. Verification happens against the data the operator exposes, not against the registry entry.
The clock is fixed. The passport mandate applies from 18 February 2027 under Reg (EU) 2023/1542 for EV, LMT, and industrial batteries above 2 kWh.
The Battery DPP introduces new expectations around battery data, traceability, sustainability information and digital access across the battery lifecycle.
Our eBook breaks down the key requirements and practical considerations businesses need to understand as they prepare for implementation.
What Battery DPP Architecture Means Under Regulation (EU) 2023/1542
Battery DPP architecture is the technical blueprint that links a physical battery to a structured, machine-readable record of its lifecycle data. Rather than one giant government database, the design is decentralized. The battery carries a data carrier, usually a QR code, that resolves to a persistent unique identifier. That identifier points to the data records held by the economic operator who placed the battery on the market, and to a lightweight EU registry that stores the identifier so market-surveillance authorities can find the passport.
The obligation is now fixed in law. Under Article 77 of Regulation (EU) 2023/1542, a battery passport becomes mandatory on 18 February 2027 for electric-vehicle batteries, light-means-of-transport batteries, and industrial batteries with a capacity above 2 kWh. Stationary battery energy storage systems above 2 kWh sit inside the industrial scope rather than a separate legal category, and automotive batteries map onto the EV scope. The economic operator placing the battery on the market carries responsibility for the accuracy and completeness of the passport data.
So when a team asks how battery DPP architecture works, the honest answer is that it is a coordination problem before it is a software problem. The data lives in many systems across many suppliers, and the architecture is what makes those fragments resolvable through a single identifier.
Does Your Battery Fall Within the DPP Scope?Understand which batteries require a Digital Product Passport and what businesses need to prepare.
Battery DPP Architecture: The Four Layers Explained
The cleanest way to reason about battery DPP architecture is as four stacked layers, each with a distinct job. Get the layers separated in your head and most of the confusion in vendor conversations disappears.
Layer one: the data carrier and unique identifier
The physical battery carries a data carrier, in practice a QR code, printed or labelled on the pack. Scanning it resolves to a persistent unique identifier. The identifier is the root node of the whole passport: it does not change over the battery’s life, and every other layer links back to it. This mirrors the principle the ESPR sets out in Article 10, where the passport must be connected through a data carrier to a persistent unique product identifier.
Layer two: the decentralized data layer
This is where the real data sits. Carbon footprint, chemistry, recycled content, state of health, and supply-chain due-diligence declarations are not shipped to a central EU server. They stay with the economic operators who generate them, reachable through the identifier. A decentralized battery DPP architecture avoids a single point of failure and lets operators protect commercially sensitive information behind access rights, which the regulation explicitly requires.
Layer three: the registry and search
A central EU registry does exist, but it is deliberately thin. It stores the unique identifiers and a small set of reference data so that customs and market-surveillance authorities can find a passport and confirm it exists. It does not store proof of compliance. Verification always happens against the data the operator exposes, not against the registry entry, and designing your battery DPP architecture around that distinction saves a lot of rework later.
Layer four: access rights and interoperability
Different actors see different slices. A recycler needs dismantling and chemistry data, a regulator needs due-diligence declarations, and a customer sees a public subset. Battery DPP architecture has to enforce these access tiers while staying interoperable with legacy identification systems, so data can move between manufacturers, regulators, recyclers, and second-life operators without a custom integration for every pair.
What Does Battery DPP Compliance Really Require?Understand the key data, documentation and compliance requirements for building a Battery Digital Product Passport.
How GS1 Standards Fit Into Battery DPP Architecture
GS1 standards are what turn battery DPP architecture from a concept into something that works across a multi-tier supply chain. Four pieces do most of the work. A Global Trade Item Number (GTIN) identifies the battery model or batch. A Global Location Number (GLN) identifies each supplier and production site. EPCIS, the event standard, records lifecycle events such as production, shipment, transformation, and recycling in a machine-readable format every partner can read. GS1 Digital Link is the resolver that turns the identifier on the QR code into a web address the data can be reached from.
Event-based traceability is the part most teams underestimate. Instead of a static file, the passport becomes a running record of what happened to the battery and when. That is why battery DPP architecture built on EPCIS scales: each partner contributes events against the same identifier, and the passport assembles itself from those contributions rather than from one supplier filling in a spreadsheet at the end.
Battery DPP Architecture: Manual Assembly vs a Platform Approach
Here is where the pain shows up. Most teams first try to assemble battery DPP architecture by hand, stitching supplier emails, spreadsheets, and internal databases into something that resembles a passport. It holds together until the first audit, or the first supplier who cannot produce the right identifier or event data on request. Fragmented supplier data, manual reporting, and missing identifiers are the three failure points that surface every time.
A platform approach inverts the problem. The TraceX Battery DPP platform captures lifecycle events via EPCIS, manages GS1 identifiers across suppliers, and generates audit-ready, passport-compliant outputs, so the architecture is built once and maintained continuously rather than reconstructed before every deadline. For a fifteen-year asset like an industrial battery, building the architecture correctly at design time is far cheaper than retrofitting a data layer onto batteries that were never instrumented to provide it.
Preparing your Battery DPP strategy?
Talk to TraceX about building a connected, DPP-ready data and traceability foundation.
Manual GTIN/GLN tracking in spreadsheets, prone to collisions
Centralized GS1 identifier management across suppliers
Lifecycle event capture
Emailed updates, reconstructed after the fact
EPCIS event capture at each supply-chain step
Supplier data
Chased per deadline, inconsistent formats
Automated supplier onboarding and structured data intake
Access control
All-or-nothing file sharing
Role-based access tiers per stakeholder
Audit readiness
Rebuilt manually before each audit
Audit-ready, DPP-compliant export on demand
Time to a working passport
Weeks of assembly per batch
Continuous, assembles from events
One data layer, many regulations. The strongest battery DPP architecture is not a single-purpose passport builder. It is one traceability data layer that already carries the identifiers, sites, and lifecycle events, then serves the battery passport, carbon-footprint declarations, and due-diligence reporting from the same foundation. Teams that build the passport as a bolt-on rebuild it for every new obligation. Teams that build the data layer once serve 2023/1542 today and the next ESPR product category tomorrow.
How to Evaluate Battery DPP Architecture for Your Supply Chain
If you are comparing vendors or deciding whether to build in-house, run any battery DPP architecture against this checklist before committing:
Does it issue and manage persistent unique identifiers, and keep them stable across the battery’s life?
Does it capture lifecycle events with EPCIS rather than storing a static file?
Does it use GS1 identifiers (GTIN, GLN) so data is interoperable across suppliers and legacy systems?
Does it keep data decentralized with role-based access tiers, so sensitive data is protected?
Does it resolve the identifier through a standard data carrier (QR code) and GS1 Digital Link?
Does it produce an audit-ready export that maps to Regulation (EU) 2023/1542 data requirements?
Can the same data layer also serve carbon-footprint and due-diligence obligations, not just the passport?
Frequently Asked Questions (FAQ’s)
Is battery DPP architecture centralized or decentralized?
It is decentralized. The actual passport data stays with the economic operators who generate it, reachable through a persistent unique identifier. A central EU registry exists but stores only identifiers and reference data, not the full dataset and not proof of compliance.
When does the battery passport become mandatory?
18 February 2027, under Article 77 of Regulation (EU) 2023/1542, for EV batteries, light-means-of-transport batteries, and industrial batteries with a capacity above 2 kWh.
Where do stationary storage systems (BESS) fit?
Battery energy storage systems above 2 kWh fall within the industrial battery scope of Regulation (EU) 2023/1542. They are not a separate legal category; they inherit the industrial-battery obligations, including the passport.
What is the role of the unique identifier?
It is the root node of the architecture. The data carrier resolves to it, the registry stores it, and every data record links back to it. It stays constant across the battery’s life, which is what lets a decentralized system stay coherent.
Why does EPCIS matter for battery DPP architecture?
EPCIS is the standard that structures lifecycle events (production, shipment, transformation, recycling) in a machine-readable, interoperable way. It lets each supply-chain partner contribute events against the same identifier, so the passport assembles from real events instead of a single spreadsheet.
Does the EU registry verify that my data is compliant?
No. The registry confirms a passport exists and helps authorities locate it. Verification happens against the data you expose through the identifier, so accuracy and completeness remain the placing operator’s responsibility.
Do due-diligence obligations start at the same time as the passport?
The supply-chain due-diligence obligations were postponed to 18 August 2027 via Regulation (EU) 2025/1561, later than the 18 February 2027 passport date. Confirm the current position at EUR-Lex before relying on either date.
Start using TraceX
Transparency, Trust, & Success for your Climate Journey.
We use cookies on our website to give you the most relevant experience by remembering your preferences and repeat visits. By clicking “Accept All”, you consent to the use of ALL the cookies. However, you may visit "Cookie Settings" to provide a controlled consent.
This website uses cookies to improve your experience while you navigate through the website. Out of these, the cookies that are categorized as necessary are stored on your browser as they are essential for the working of basic functionalities of the website. We also use third-party cookies that help us analyze and understand how you use this website. These cookies will be stored in your browser only with your consent. You also have the option to opt-out of these cookies. But opting out of some of these cookies may affect your browsing experience.
Necessary cookies are absolutely essential for the website to function properly. These cookies ensure basic functionalities and security features of the website, anonymously.
Cookie
Duration
Description
cookielawinfo-checkbox-analytics
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Analytics".
cookielawinfo-checkbox-functional
11 months
The cookie is set by GDPR cookie consent to record the user consent for the cookies in the category "Functional".
cookielawinfo-checkbox-necessary
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookies is used to store the user consent for the cookies in the category "Necessary".
cookielawinfo-checkbox-others
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Other.
cookielawinfo-checkbox-performance
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Performance".
viewed_cookie_policy
11 months
The cookie is set by the GDPR Cookie Consent plugin and is used to store whether or not user has consented to the use of cookies. It does not store any personal data.
Functional cookies help to perform certain functionalities like sharing the content of the website on social media platforms, collect feedbacks, and other third-party features.
Performance cookies are used to understand and analyze the key performance indexes of the website which helps in delivering a better user experience for the visitors.
Analytical cookies are used to understand how visitors interact with the website. These cookies help provide information on metrics the number of visitors, bounce rate, traffic source, etc.
Advertisement cookies are used to provide visitors with relevant ads and marketing campaigns. These cookies track visitors across websites and collect information to provide customized ads.
Download the 2026 Traceability Scorecard and Benchmark Your Supply Chain Across 10 Critical Capabilities.
Download our eBook
Don’t Wait for an Audit to Find Your EUDR Gaps
The 2026 Simplification Package changes how HS codes, DDS pass-through and geolocation rules apply to you. Get the free guide and 20-point readiness checklist before enforcement catches you unprepared.